xPGuard installs and manages ModSecurity rules on Apache and LiteSpeed: the OWASP Core Rule Set, WordPress and CMS hardening, virtual patches for known plugin vulnerabilities and bad-bot blocking. Legitimate traffic is protected by automatic false-positive learning and per-domain controls.
- OWASP CRS plus xPGuard rule packages (web shells, scanners, crawlers, virtual patches)
- WordPress, WooCommerce, admin panel and REST API exclusions built in
- Automatic false-positive protection and per-site rule allow lists
- Bad-bot blocker and a CAPTCHA challenge for suspicious visitors on login pages
- WAF logs with filters, export and one-click whitelisting
- Per-domain ModSecurity on/off for cPanel accounts
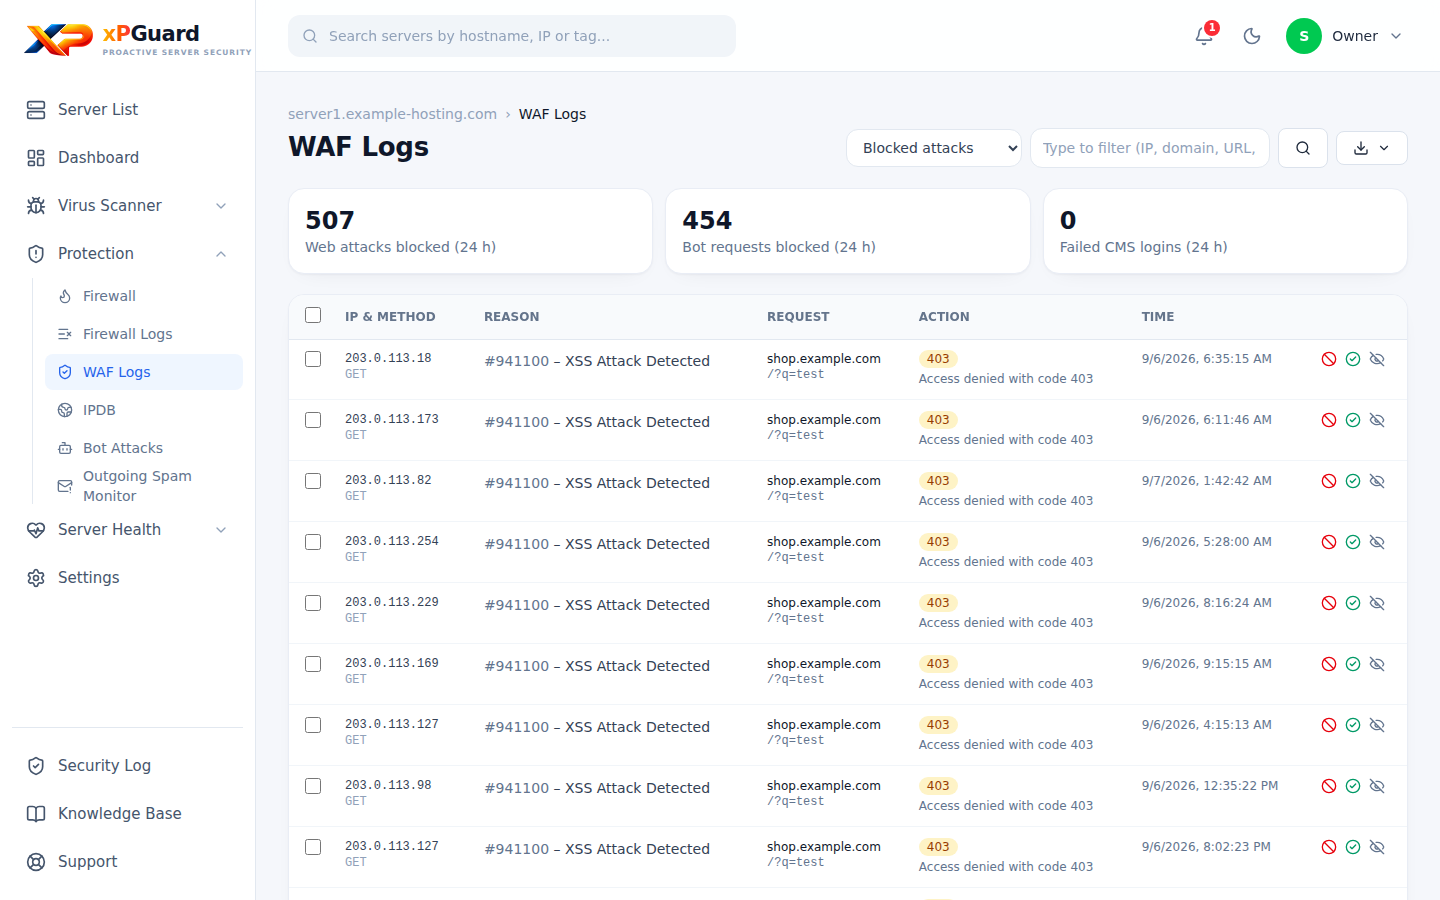
Blocked web attacks with rule, domain and visitor details
More Features
Real-time Malware Scanner
Detect and remove malware, web shells and backdoors the moment files change.
Advanced Firewall
Block brute force, port scans and attacks with a smart nftables/iptables firewall.
IP Reputation (IPDB)
A shared blocklist: an attacker seen on one server is blocked on all of them.
CMS Threat Detection
Find vulnerable plugins, themes and database injections in WordPress and other CMS.
Mail Protection
Stop spam, phishing and outgoing abuse on Exim with RBLs and smart filters.