Every upload, FTP transfer, File Manager change and CMS update is scanned in real time. Signatures, heuristics and machine learning catch web shells, backdoors, droppers, spam mailers and phishing kits, and the scanner cleans or quarantines them before they can run.
- Real-time scanning of every home directory (inotify), plus scheduled quick and full scans
- Own signature engine, heuristics and fleet-learned web shell names
- Surgical cleaning: injected code removed, the rest of the file kept
- WordPress core files replaced with the official copy; hacked .htaccess files cleaned
- Quarantine with one-click restore, ignore lists and full scanner logs
- Low-priority scan engine that slows down automatically when the server is busy
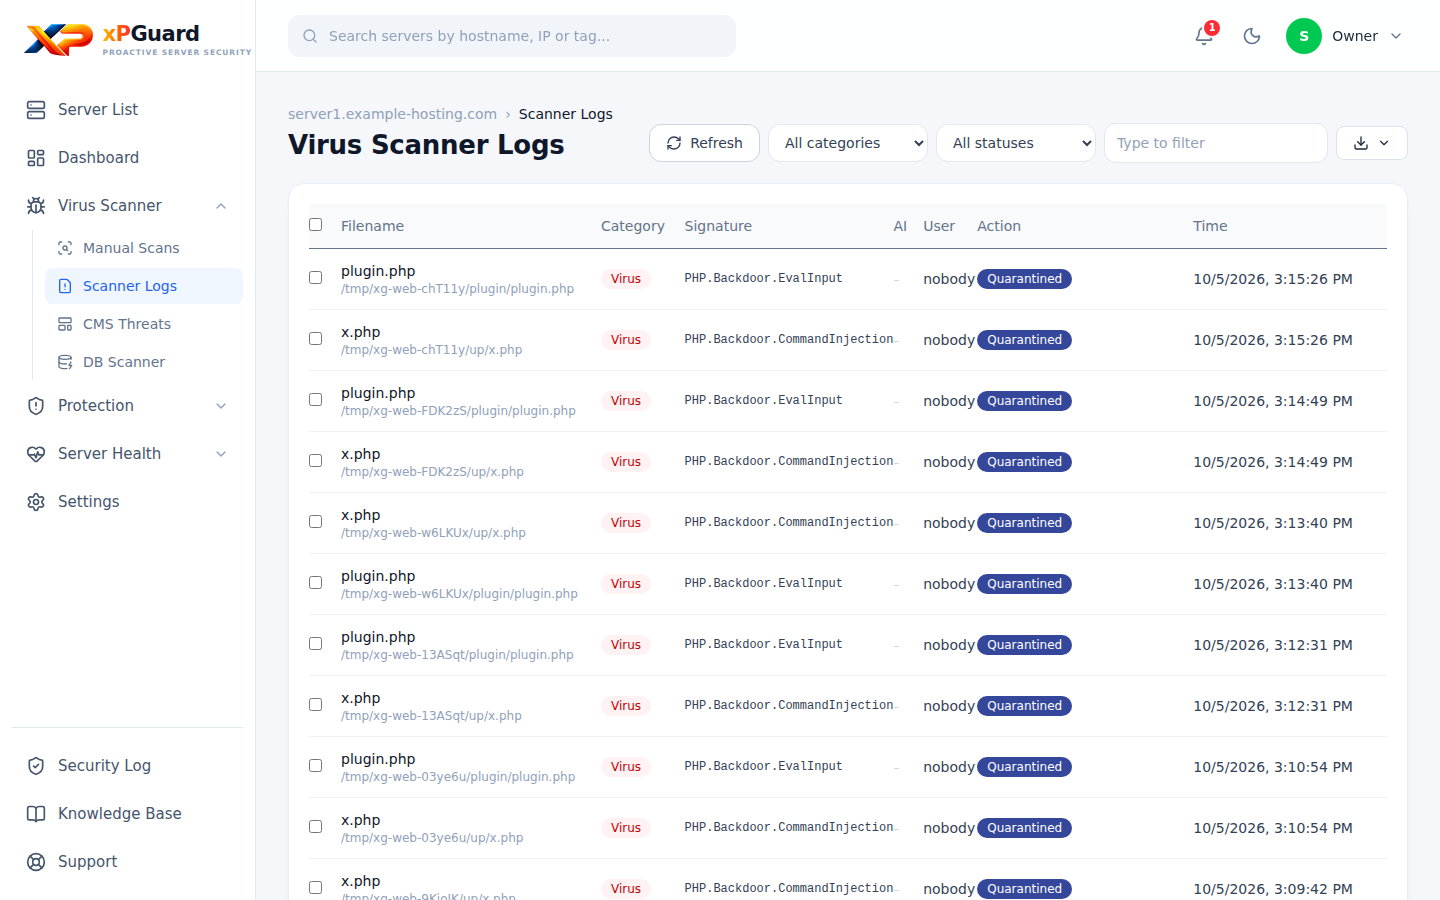
Detections with the action taken: quarantined, cleaned or restored
More Features
Advanced Firewall
Block brute force, port scans and attacks with a smart nftables/iptables firewall.
Web Application Firewall
ModSecurity rules with OWASP CRS, WordPress hardening and automatic false-positive protection.
IP Reputation (IPDB)
A shared blocklist: an attacker seen on one server is blocked on all of them.
CMS Threat Detection
Find vulnerable plugins, themes and database injections in WordPress and other CMS.
Mail Protection
Stop spam, phishing and outgoing abuse on Exim with RBLs and smart filters.