Brute-force bots hammer wp-login.php, xmlrpc.php, cPanel and admin URLs all day. xPGuard sends suspicious visitors to a fast CAPTCHA page first: real people pass in a second and go straight back to the site, bots never reach PHP or your database. Trusted visitors are never challenged.
- Protects WordPress, Joomla, Magento and other admin and login URLs
- Only suspicious visitors are challenged: high IPDB risk, brute-force patterns, WAF hits
- Privacy-friendly proof-of-work check (ALTCHA) or Cloudflare Turnstile
- Search engines, uptime monitors and payment gateways are always allowed
- A passed visitor is remembered across every protected server
- Branded page with three designs and a countdown back to the site
- Pass, fail and refuse statistics in the control panel
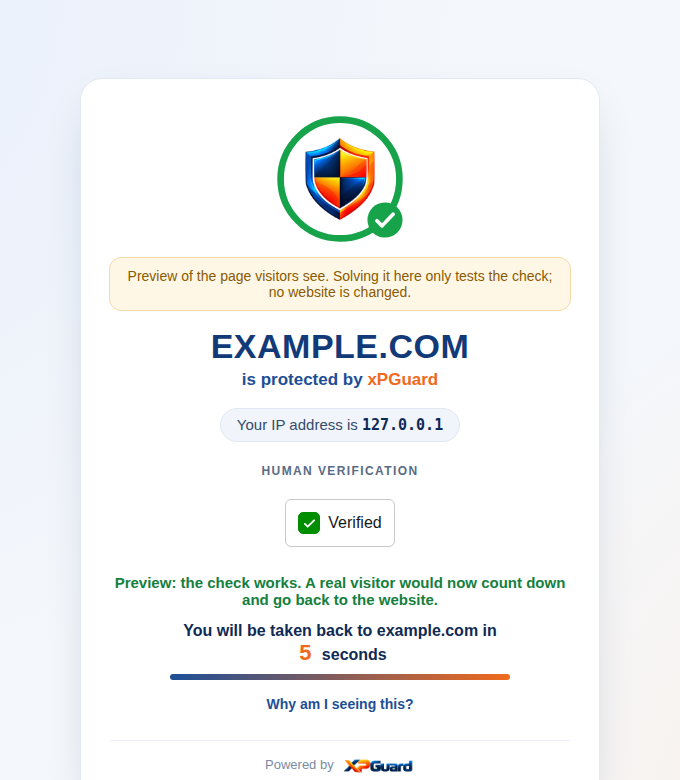
What a suspicious visitor sees before a login page
More Features
Real-time Malware Scanner
Detect and remove malware, web shells and backdoors the moment files change.
Advanced Firewall
Block brute force, port scans and attacks with a smart nftables/iptables firewall.
Web Application Firewall
ModSecurity rules with OWASP CRS, WordPress hardening and automatic false-positive protection.
IP Reputation (IPDB)
A shared blocklist: an attacker seen on one server is blocked on all of them.
CMS Threat Detection
Find vulnerable plugins, themes and database injections in WordPress and other CMS.